Why Festive Season Is a Peak Time for Cyber Fraud Targeting Indian Businesses
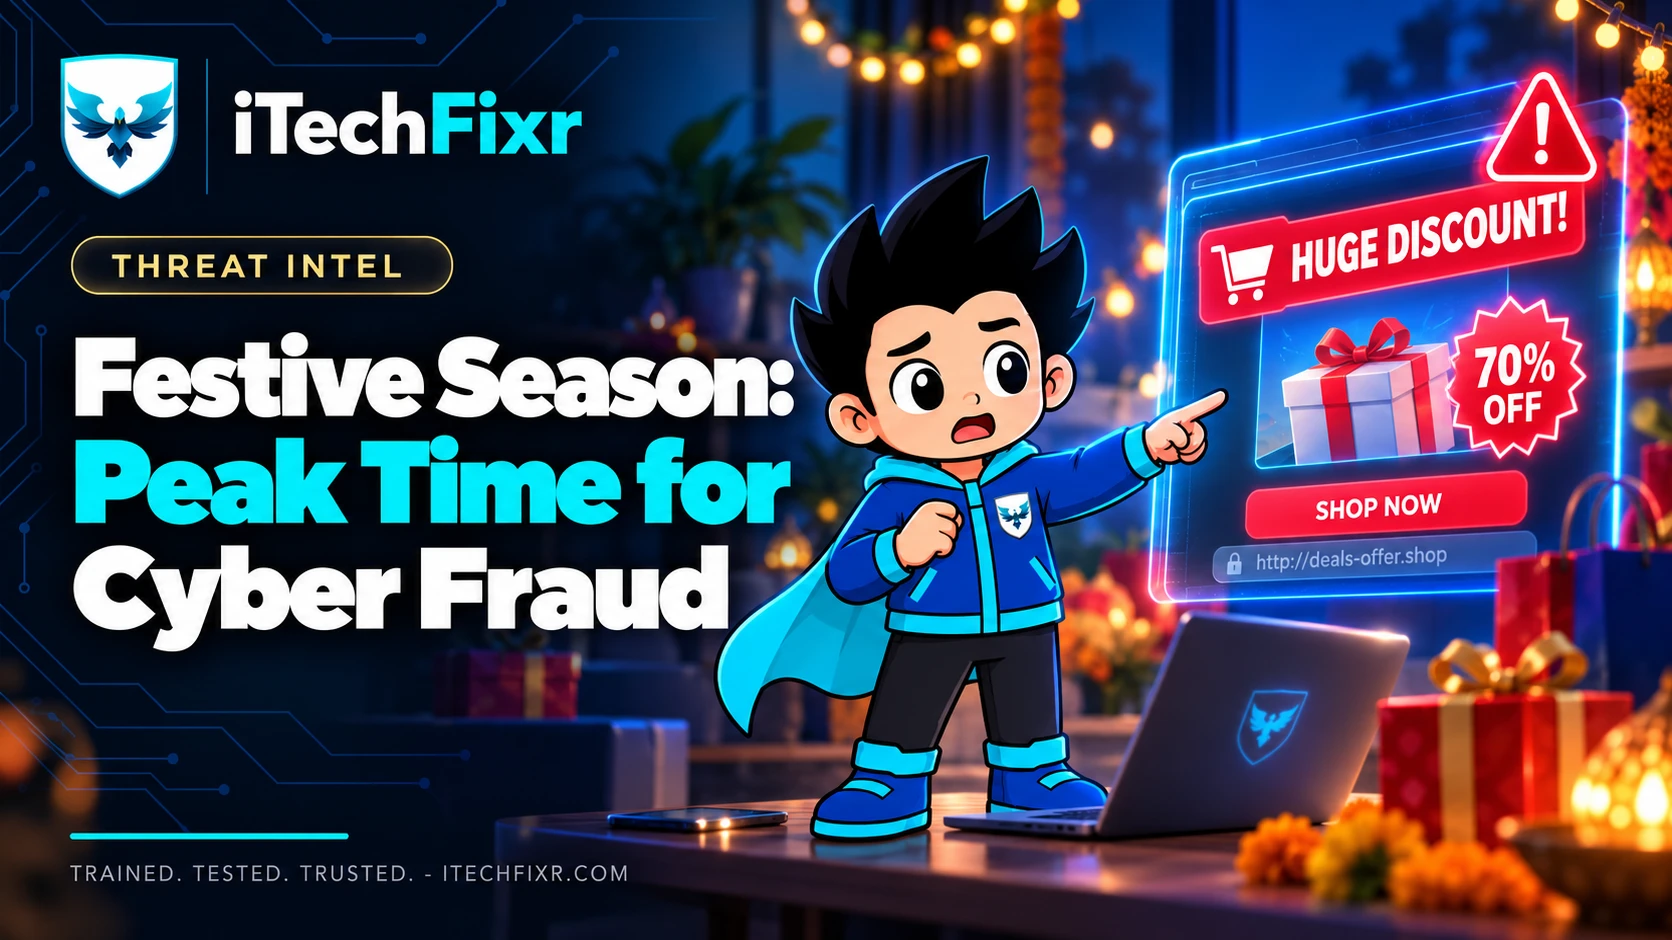
Higher transaction volumes, temporary staff, and distracted teams make the festive sales season a predictable spike period for fraud attempts.
💡 In Simple Terms (For Beginners)
During festive sales season, businesses process more transactions, hire more temporary staff, and move faster than usual — all of which fraudsters specifically time their attempts around, since the usual checks are more likely to be rushed.
- Higher transaction volume during festive season makes individual fraudulent transactions easier to miss.
- Temporary seasonal staff often haven't received the same security training as permanent employees.
- Fraud attempts specifically increase around known high-volume periods, not randomly distributed year-round.
THREAT INTEL · October 24, 2026 · 6 min read · By Hardik Patel
Why is festive season a peak time for cyber fraud targeting Indian businesses? Higher transaction volumes, temporary seasonal staff without full security training, and generally faster-paced operations combine to make festive sales periods a predictable spike window for both payment fraud and phishing attempts.
Why Transaction Volume Itself Is a Risk Factor
A higher volume of legitimate transactions makes individual fraudulent ones statistically easier to miss — the same anomaly-detection habits that work well at normal volume become harder to apply consistently when transaction counts spike significantly above baseline.
The Seasonal Staff Gap
Temporary staff hired specifically for the festive rush often haven't received the same security training and verification habits as permanent employees, making them a specifically softer target for social engineering attempts timed to exploit this exact gap.
This connects directly to the new employee onboarding principle — the gap is larger for seasonal staff precisely because the usual onboarding time pressure is compressed even further during a hiring rush.
Practical Preparation
- Give seasonal staff a condensed but real security briefing before they start, not just operational training.
- Reinforce payment verification habits specifically before the peak period begins, when the team is less rushed to actually absorb it.
- Increase monitoring attention around known high-volume days, rather than assuming normal-volume monitoring habits scale automatically.
- Have a fast escalation path ready for the team to flag anything suspicious without needing to interrupt the sales rush to figure out who to tell.
Key Takeaways
- Higher transaction volume makes individual fraud attempts statistically easier to miss.
- Seasonal staff are a specifically softer target due to compressed or missing security training.
- Pre-season briefing and a clear escalation path are achievable, high-value preparation steps.
Frequently Asked Questions
Q: Should seasonal staff get the same full training as permanent employees?
A: A condensed version covering the highest-priority risks (payment verification, phishing basics) is more realistic than the full program, but skipping security training entirely for seasonal hires leaves a real, avoidable gap.
Q: Is this risk specific to e-commerce, or does it apply to service businesses too?
A: It applies broadly — any business with higher seasonal transaction volume, temporary staffing, or increased customer communication during festive periods faces a similar pattern, not just retail or e-commerce specifically.
How iTechFixr Can Help
Our Human Firewall training can be scheduled ahead of a business's known peak season, giving both permanent and seasonal staff a real security briefing before the rush begins.
Need Help With This?
Talk to Hardik directly about your organisation's cybersecurity needs — get a tailored response within 24 hours.
